CYBERSECURITY

Protect what matters. Understand where you’re exposed.

We help organizations identify meaningful cybersecurity risk, strengthen their technology environment, and build practical defenses around their people, systems, applications, and data.

We Can Change IT presenting findings from a client penetration testing and security assessment engagement.

Cybersecurity is not just a product you install.

Organizations depend on endpoints, cloud services, networks, applications, vendors, identities, and data that are constantly changing. Security gaps often appear between those systems—not simply because a security product is missing. Our job is to help you understand the environment, prioritize meaningful risks, and determine what actually needs to be fixed.


Security built around your environment.

Security Assessments

Evaluate your overall security posture, identify control gaps, and map defenses to industry frameworks (NIST, CIS, ISO).

Vulnerability Management

Continuous scanning, validation, and risk-based prioritization to help teams focus remediation on the vulnerabilities that matter most.

Endpoint & XDR Security

Deploy, configure, and monitor endpoint detection and response tools to improve visibility, investigation, and response across managed systems.

Security Architecture

Design and implement secure network zoning, zero-trust access controls, and resilient cloud infrastructure configurations.

External Exposure & OSINT

Analyze your public-facing footprint and use open-source intelligence to discover forgotten assets, leaks, and potential entry points.

Security Consulting

On-demand access to virtual CISO expertise, policy development, incident response readiness, and strategic security planning.
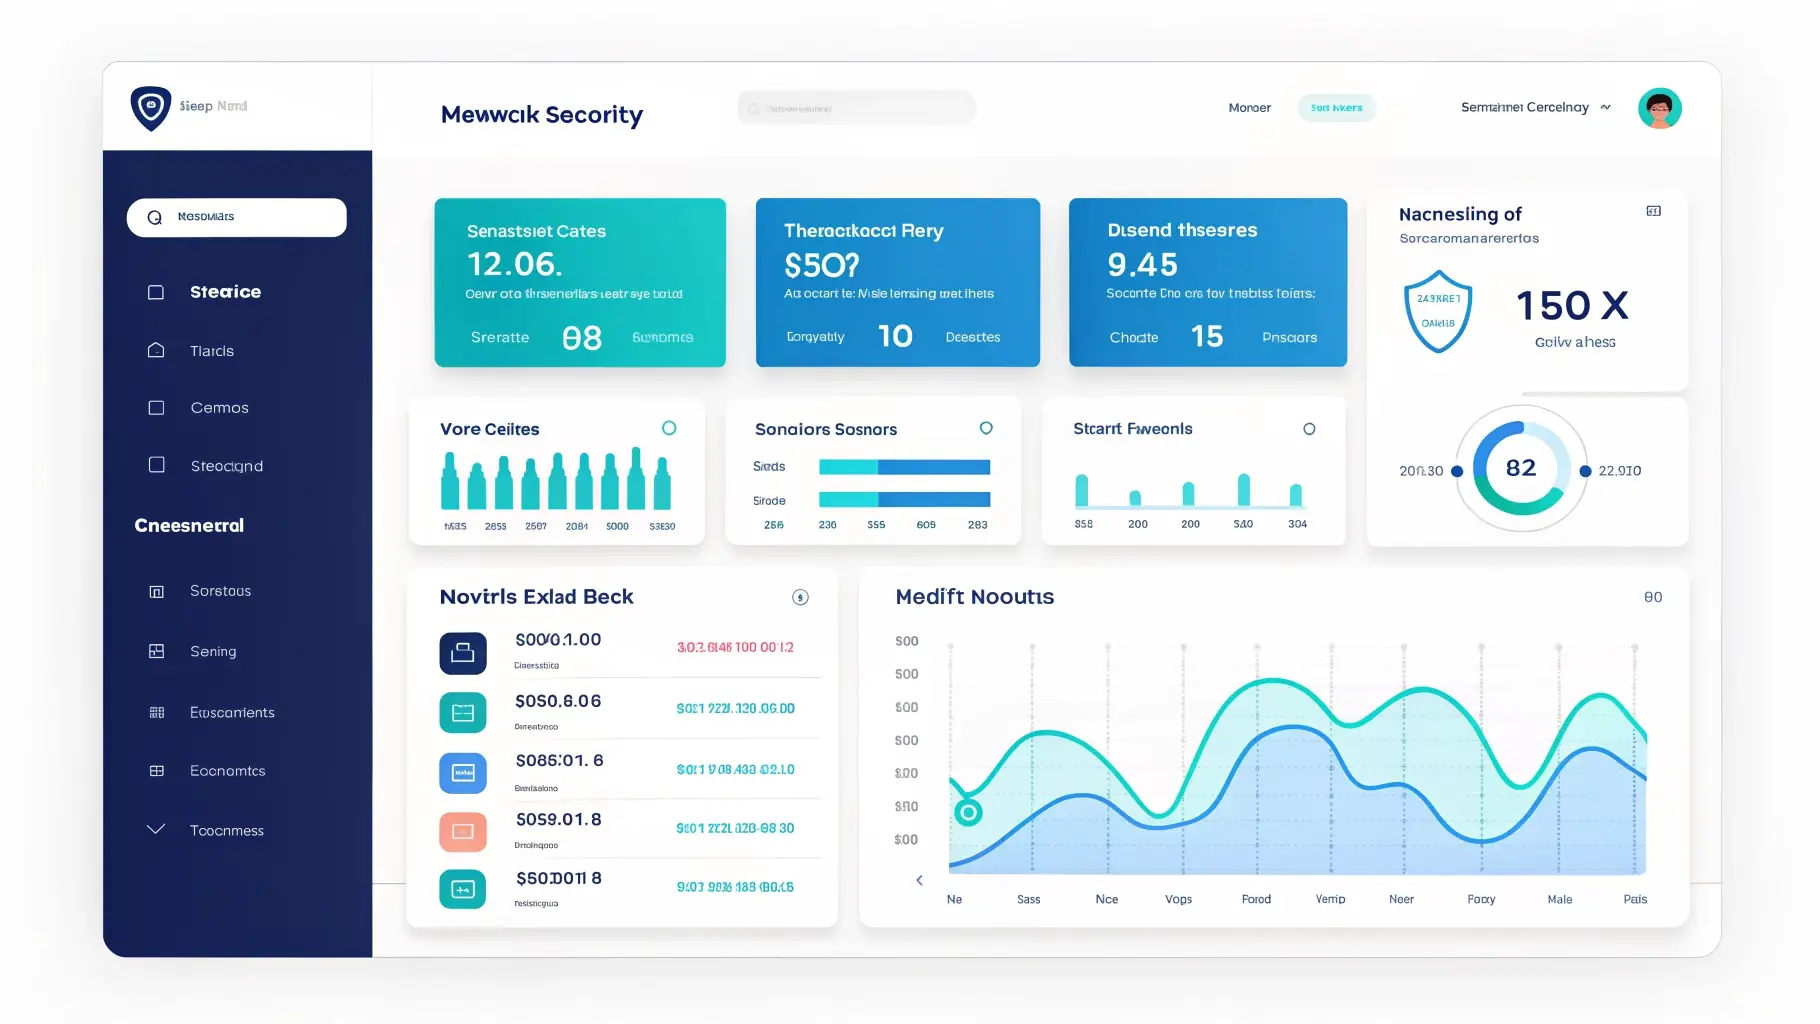
Advanced Cybersecurity Security Dashboard showing real-time endpoint status and threat vectors

Protect the devices your organization relies on every day.

Modern endpoint protection goes beyond traditional antivirus. We help organizations deploy, configure, monitor, and improve endpoint security across laptops, workstations, servers, and supported cloud workloads.

Endpoint Detection & Response

Behavioral monitoring and response workflows designed to help teams investigate and contain suspicious activity.

Threat Visibility

Centralized security visibility to help teams understand activity across managed endpoints and systems.

Policy & Configuration

Standardize security Baselines, manage patches, and seal entry configurations.

Response & Remediation

Automated response workflows can help isolate affected hosts and support remediation when appropriate.

See what an attacker can learn before they ever touch your network.

Publicly available information, exposed services, credentials from historical breaches, domains, email addresses, cloud assets, and organizational information can all contribute to an attacker’s understanding of a target.

Domain & Infrastructure Exposure

Mapping public DNS records, active subdomains, and routing configurations to pinpoint overlooked perimeter entryways.

Publicly Exposed Services

Identifying open ports, internal development consoles, database instances, and database interfaces visible online.

Credential/Breach Exposure

Locating compromised employee credentials, leaks, and cleartext passwords circulating in public and dark web repositories.

Employee & Organizational OSINT

Reviewing publicly available organizational information, email patterns, and executive profiles that may increase social-engineering exposure.

Brand & Domain Abuse

Monitoring typosquatting, lookalike hostnames, and malicious registrations constructed to deceive your customers and staff.

Attack-Surface Research

Continual exploration of third-party dependencies, legacy hosts, and software systems introducing passive threat risk.

Want to go beyond an assessment? Test the environment.

Penetration testing evaluates whether identified weaknesses can be meaningfully combined or exploited within an authorized scope. We offer internal, external, wireless, web, and targeted security testing with actionable remediation guidance.

Explore Penetration Testing
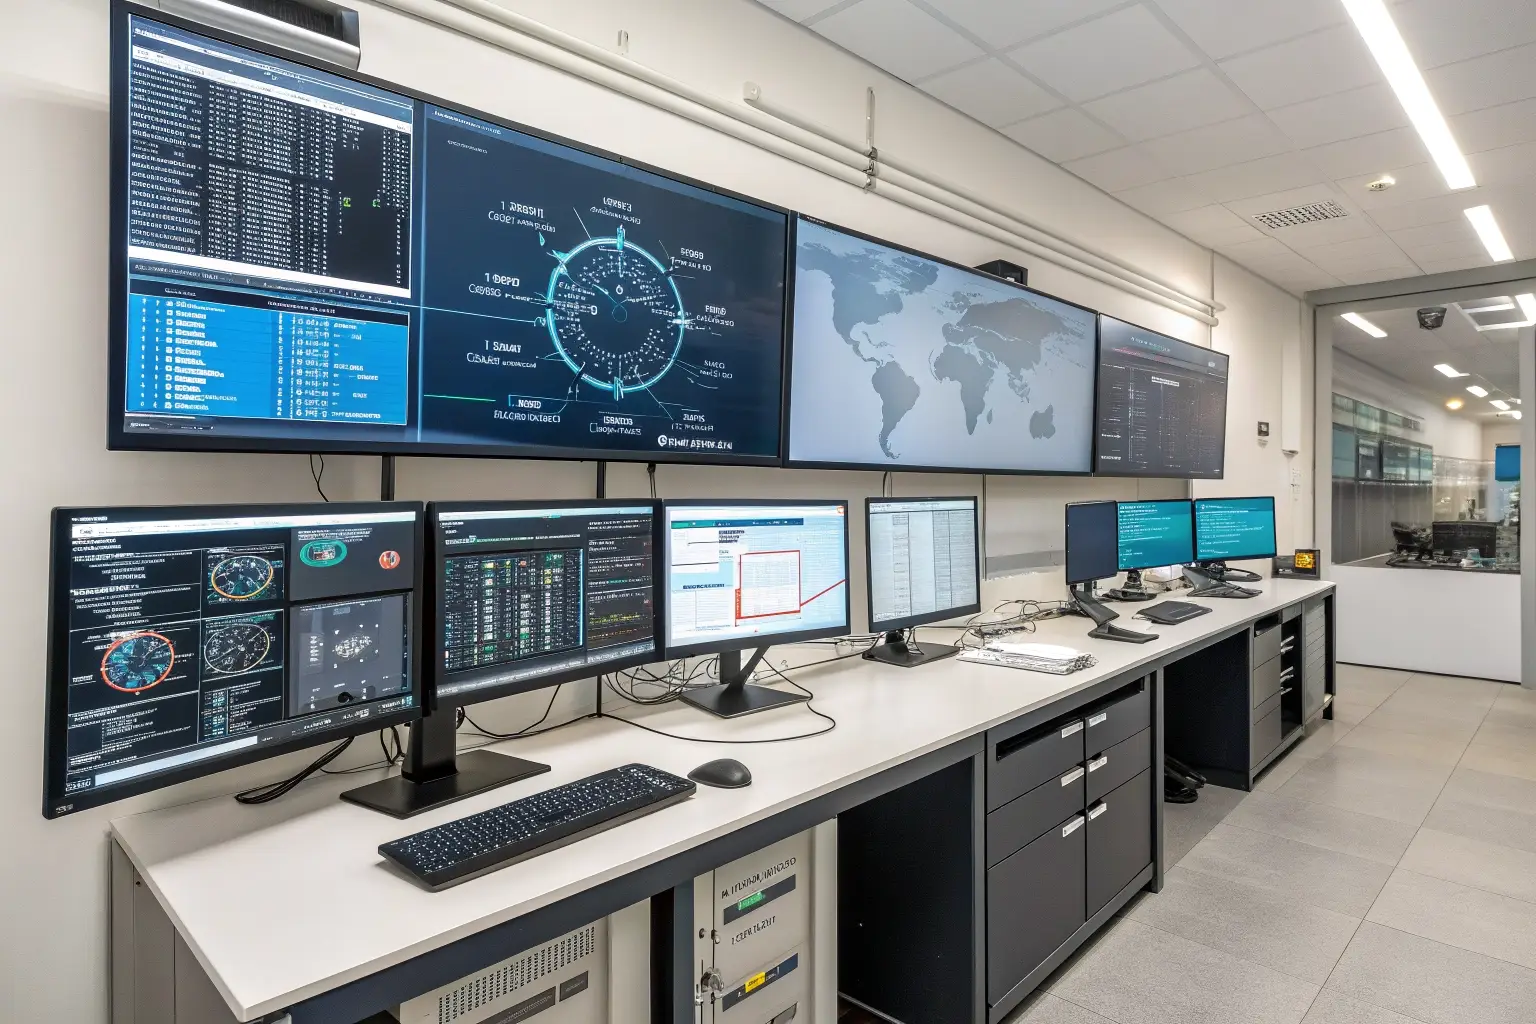
Cybersecurity professional workstation with dual screens showing diagnostic dashboards

Security works better when it is designed in from the beginning.

Whether you are modernizing an existing environment or building something new, security decisions made during architecture can prevent larger problems later.

Network segmentation

Identity & access

Endpoint architecture

Cloud security

Application security

Logging & visibility

Turn security requirements into practical technical work.

Security frameworks can provide useful structure, but organizations still need to translate requirements into real configurations, processes, architecture, documentation, and remediation work.

*Disclaimer: Reference to external frameworks (NIST, CIS, SOC 2, CMMC) does not imply endorsement or official certification. All standards remain properties of their respective trademark owners.

Supported Standards

Prioritize what matters.


01

Understand

Map compliance frameworks and specific business targets to build a clear, comprehensive technical requirement matrix.

02

Discover

Conduct a thorough assessment of technical assets, cloud architecture, local endpoints, and written policies to discover gaps.

03

Prioritize

Identify which gaps represent real-world vulnerabilities and address the highest-impact findings first to maintain operational continuity.

04

Remediate

Apply direct configuration fixes, write and standardize processes, implement network architecture adjustments, and assemble necessary documentation.

05

Validate

Re-evaluate the infrastructure continuously to verify the successful mitigation of previous gaps and generate reliable technical evidence.

What a security engagement can look like

We provide transparent, thorough cybersecurity evaluations. Here is a real-world blueprint of an exhaustive agency-level audit.


Cybersecurity + Penetration Testing

Insurance Agency Security Assessment

Scope may include the following technical security evaluations:

Request Security Assessment
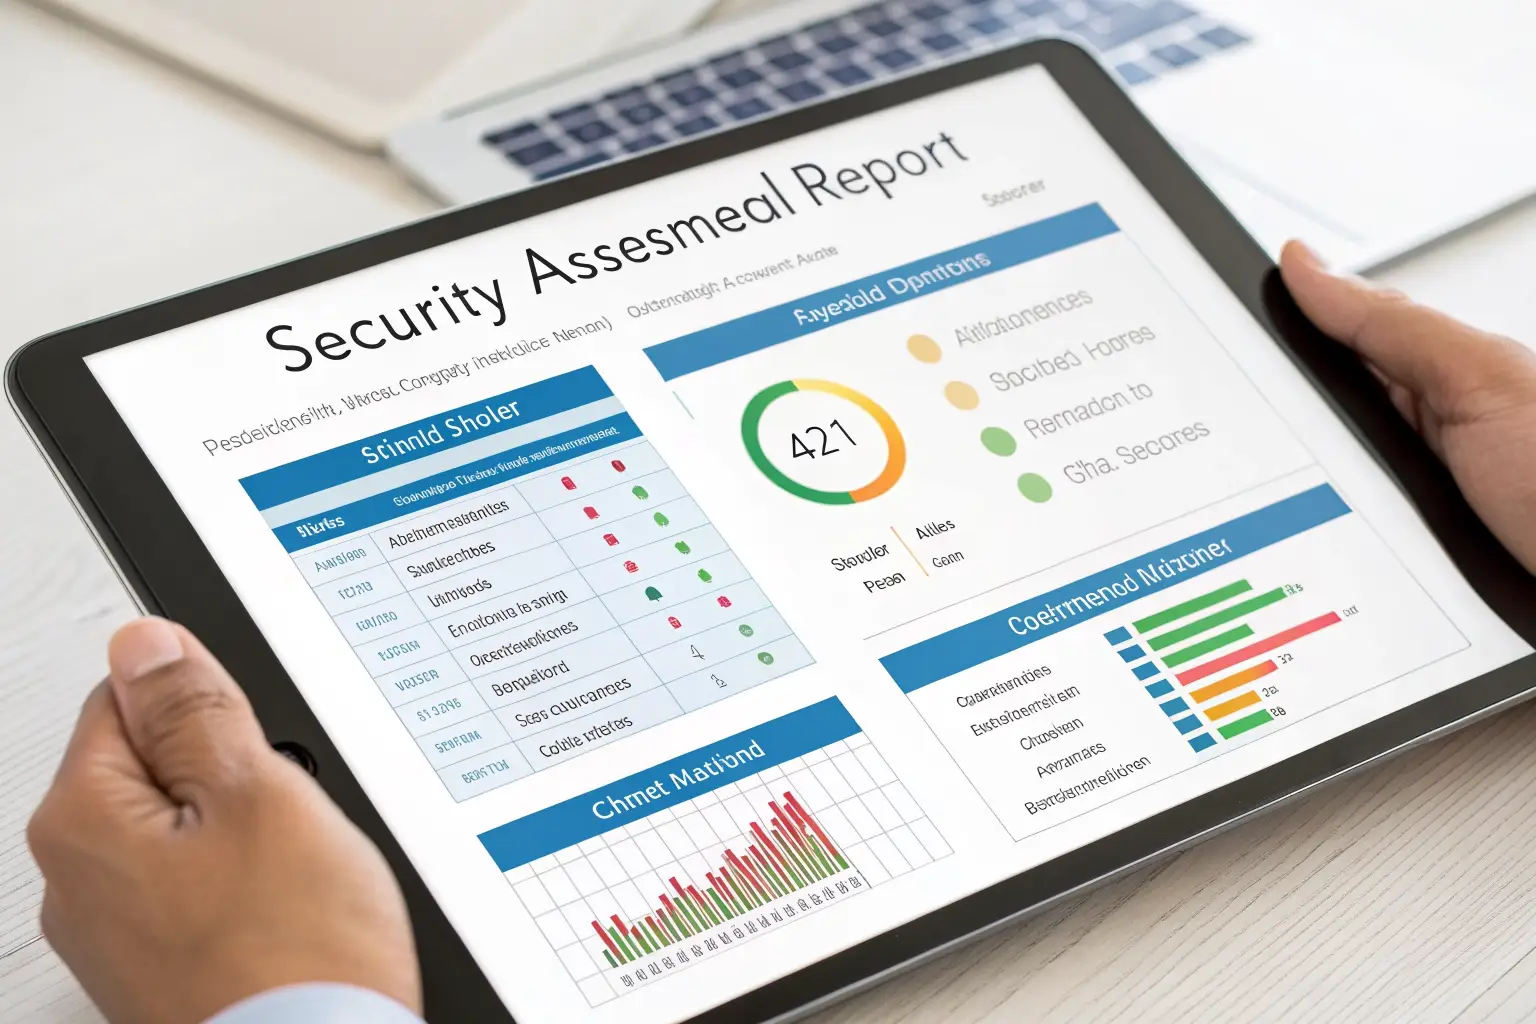
Insurance Agency Security Assessment Report Preview

Cybersecurity for organizations that need practical answers.

Small & Midsize Businesses

Practical security controls and guidance tailored for growing teams, with an emphasis on reducing risk, supporting reliable operations, and aligning safeguards with business requirements.

Schools & Education

Secure student records, defend learning portals, and maintain rigorous regulatory compliance with zero operational friction.

Insurance & Professional Services

Protect highly sensitive client financial, insurance, and personal records with robust and auditable threat protection.

Nonprofits

Safeguard donor databases and mission-critical networks using highly cost-efficient, high-impact security measures.

Security connects to the rest of your technology.

Penetration Testing

Proactively identify blindspots and systemic flaws before threat actors do. Simulate attacks against modern infrastructures.

Explore Pentesting

IT & Cloud

Safeguard cloud workspaces, implement true Zero-Trust network principles, and construct bulletproof infrastructure configurations.

Secure Your Cloud

Software & Automation

Automate routine security audits inside development pipelines. Deploy secure solutions at velocity without losing peace of mind.

Automate Security

Not sure where your biggest security risks are?

Start with a conversation about your environment. We’ll help you determine whether the right next step is an assessment, penetration test, architecture review, endpoint project, or another security improvement.